
Certifications
Cybersecurity is a matter of trust. That is why DeltaSecure is certified by independent, accredited testing bodies.
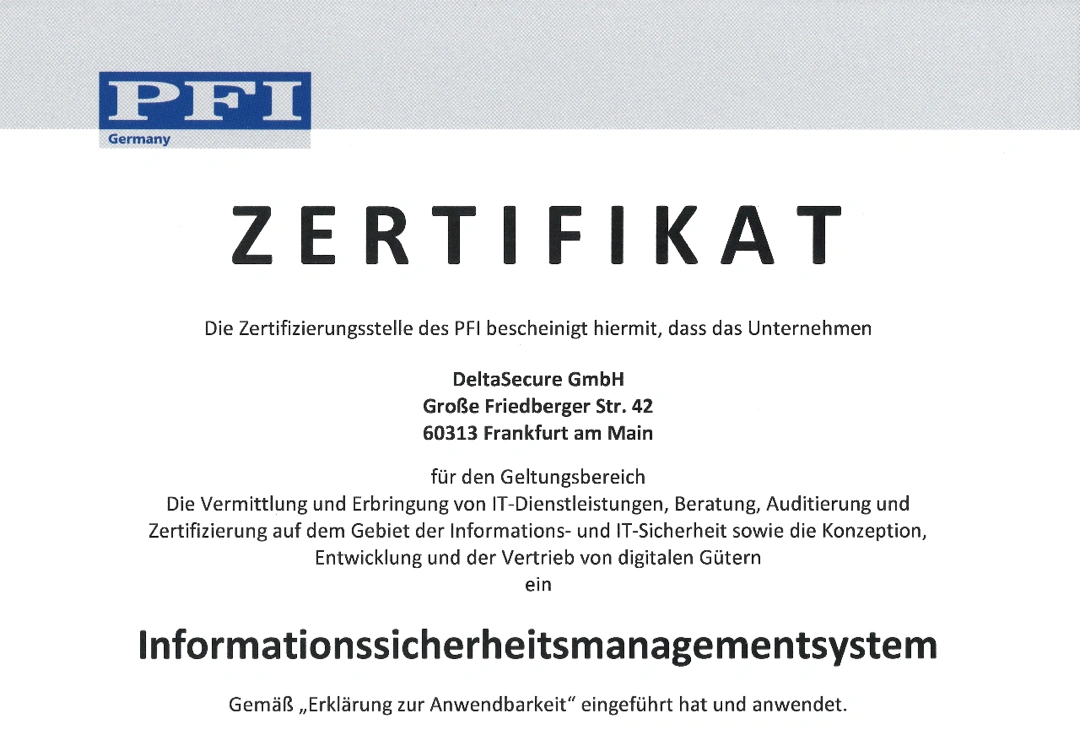
DIN EN ISO/IEC 27001
Scope covers the entire company: Provision and delivery of IT services, consulting, auditing, and certification in information and IT security, as well as the design, development, and distribution of digital goods.
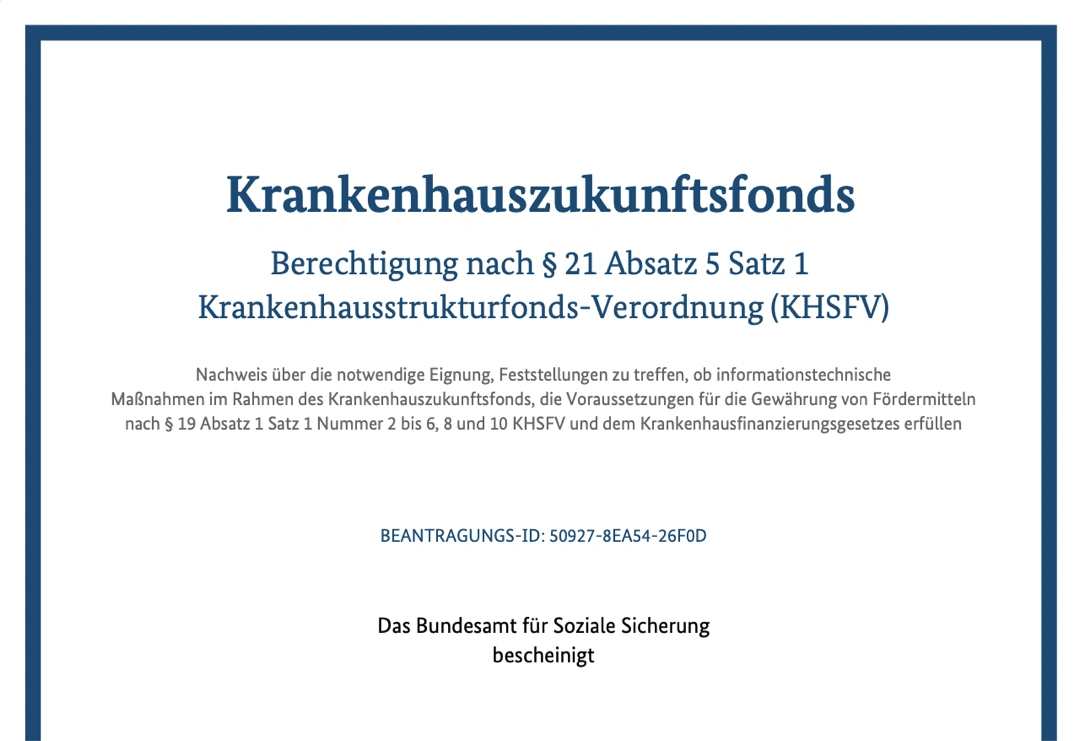
Authorization per Section 21 (5) Sentence 1 Hospital Structure Fund Regulation
Certification to meet the prerequisites for granting funding under the Hospital Structure Fund Regulation and the Hospital Financing Act.
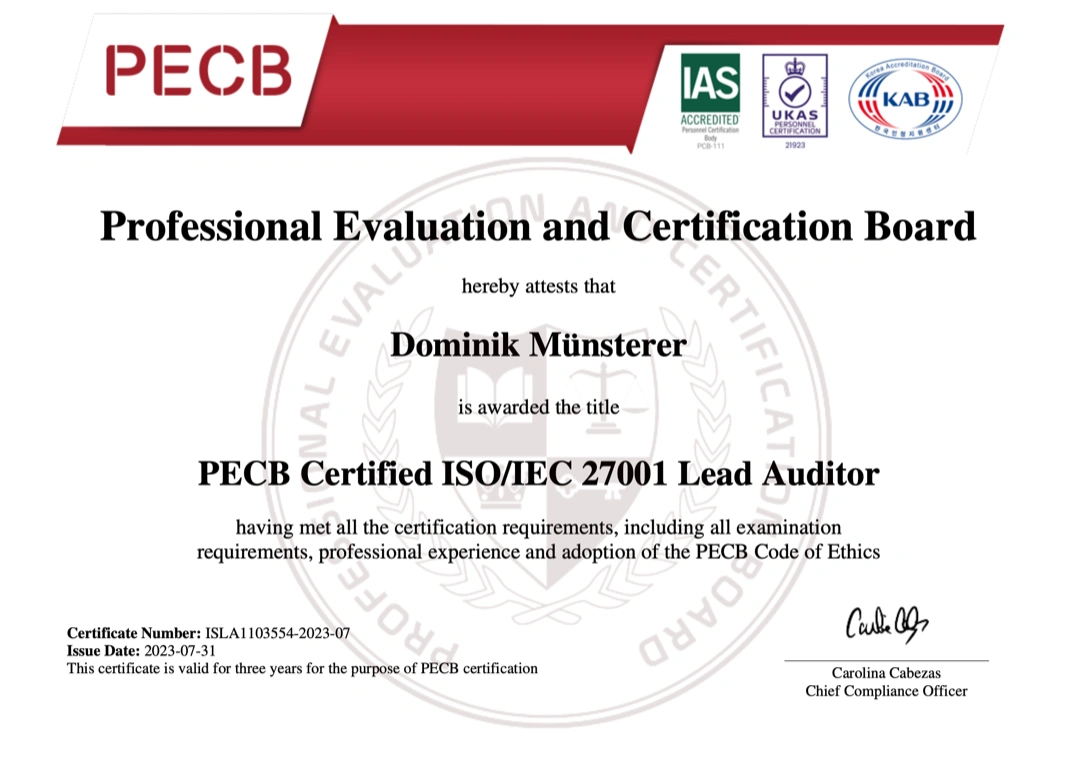
PECB Certification as ISO 27001 Lead Auditor
The ISO 27001 Lead Auditor certification enables Dominik Munsterer to conduct ISO 27001 audits for accredited testing bodies.
MicroFocus (formerly HP Enterprise) Certified Expert
Expert certification by the SIEM vendor MicroFocus (now OpenText, formerly HP Enterprise).
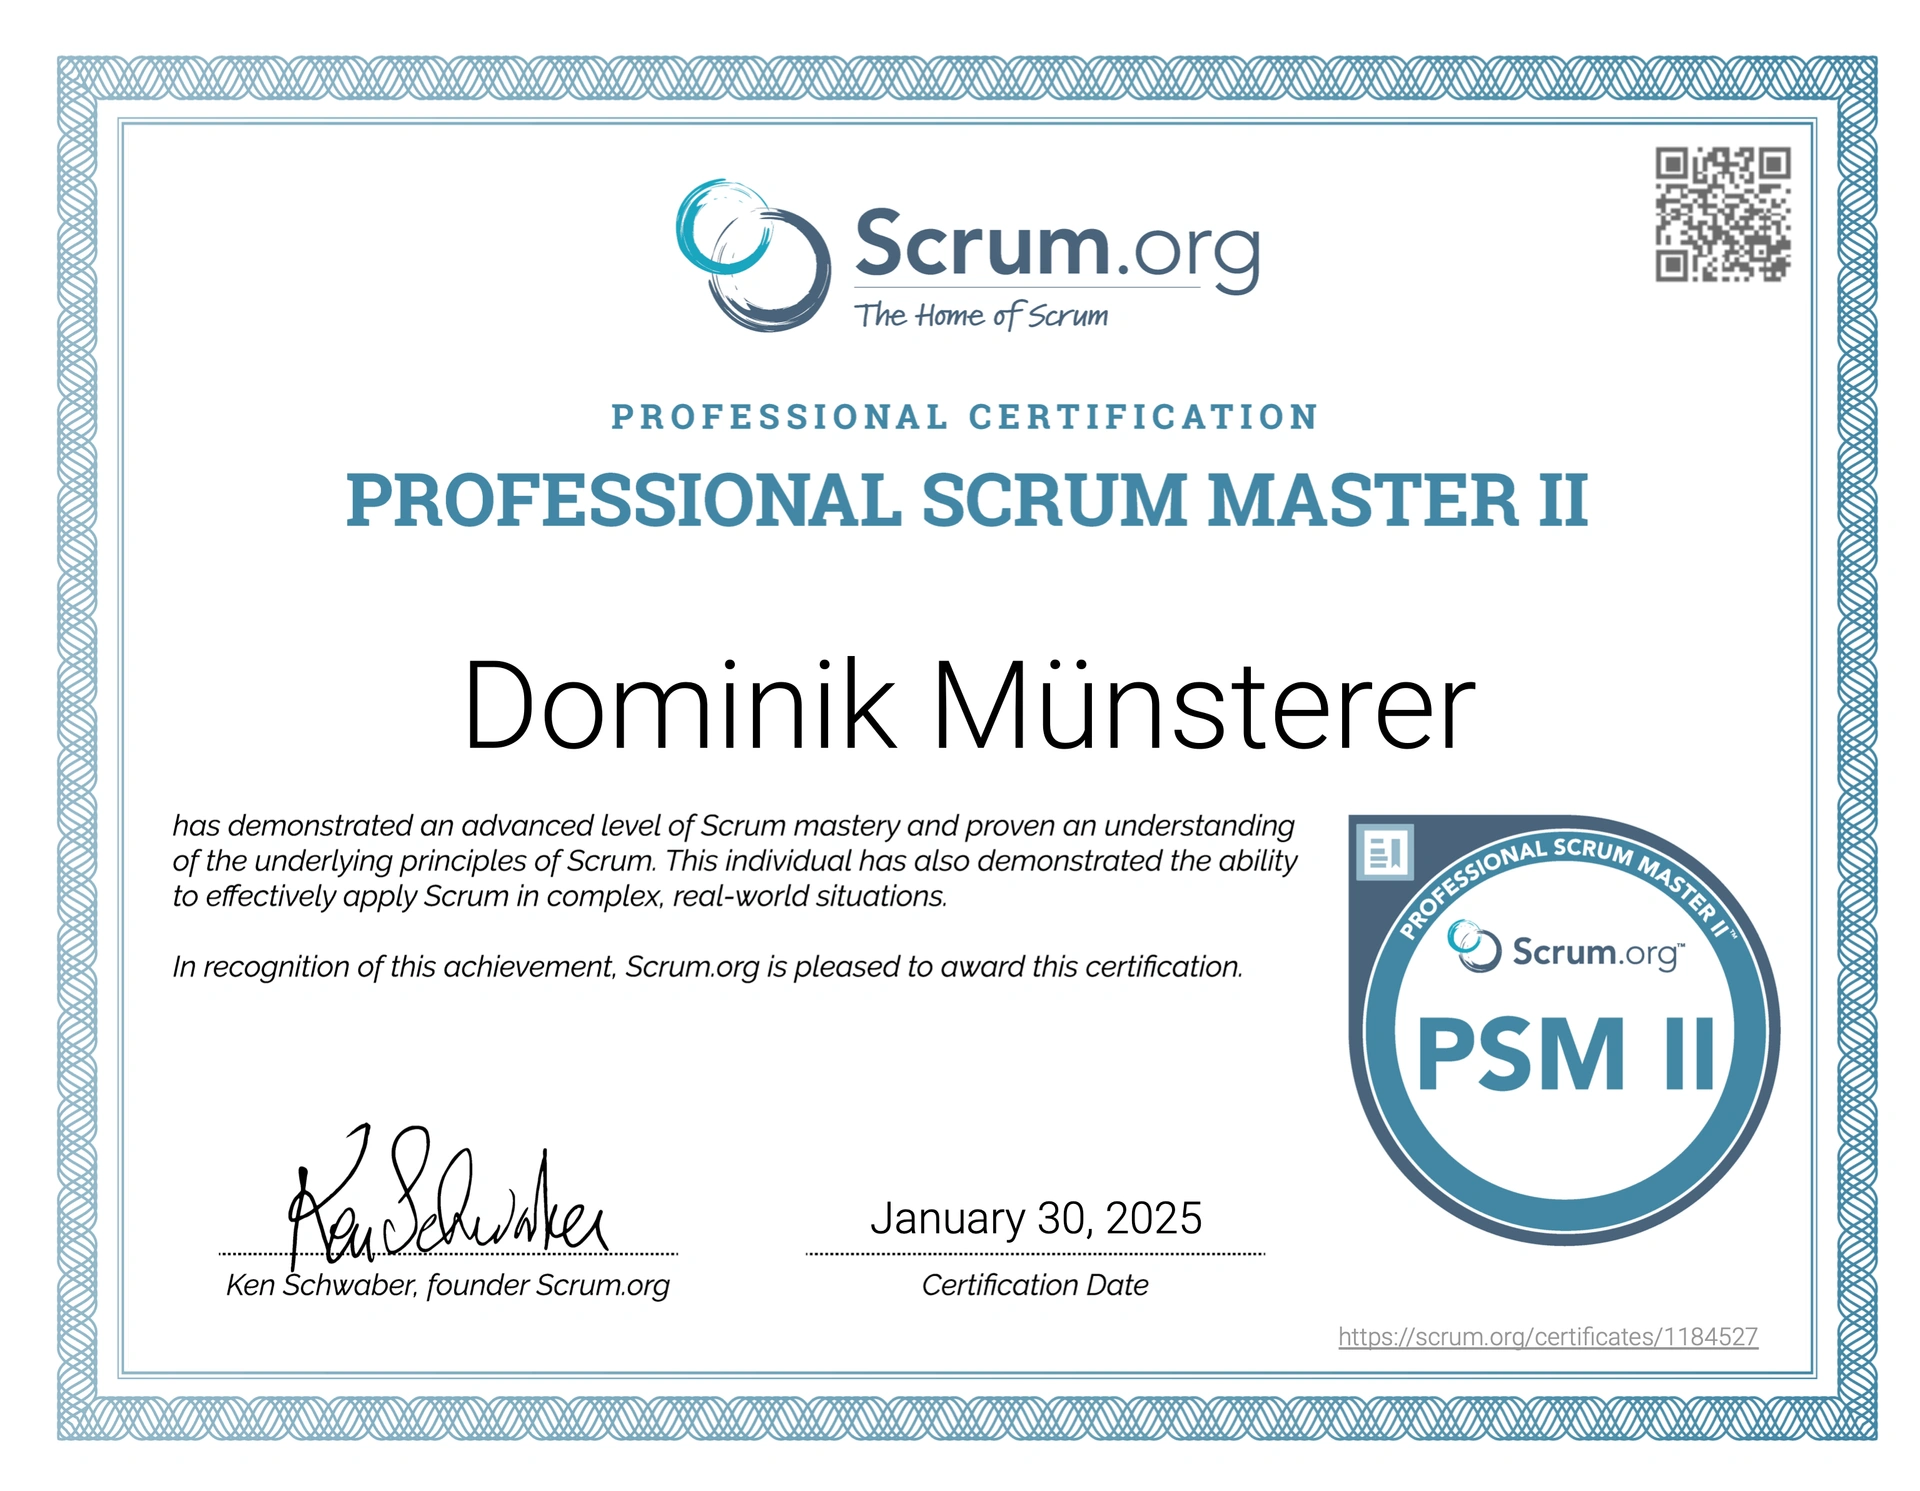
Professional Scrum Master II (PSM II)
The Professional Scrum Master II certification confirms advanced skills in Scrum methodology, servant leadership, and successful facilitation of complex agile teams.
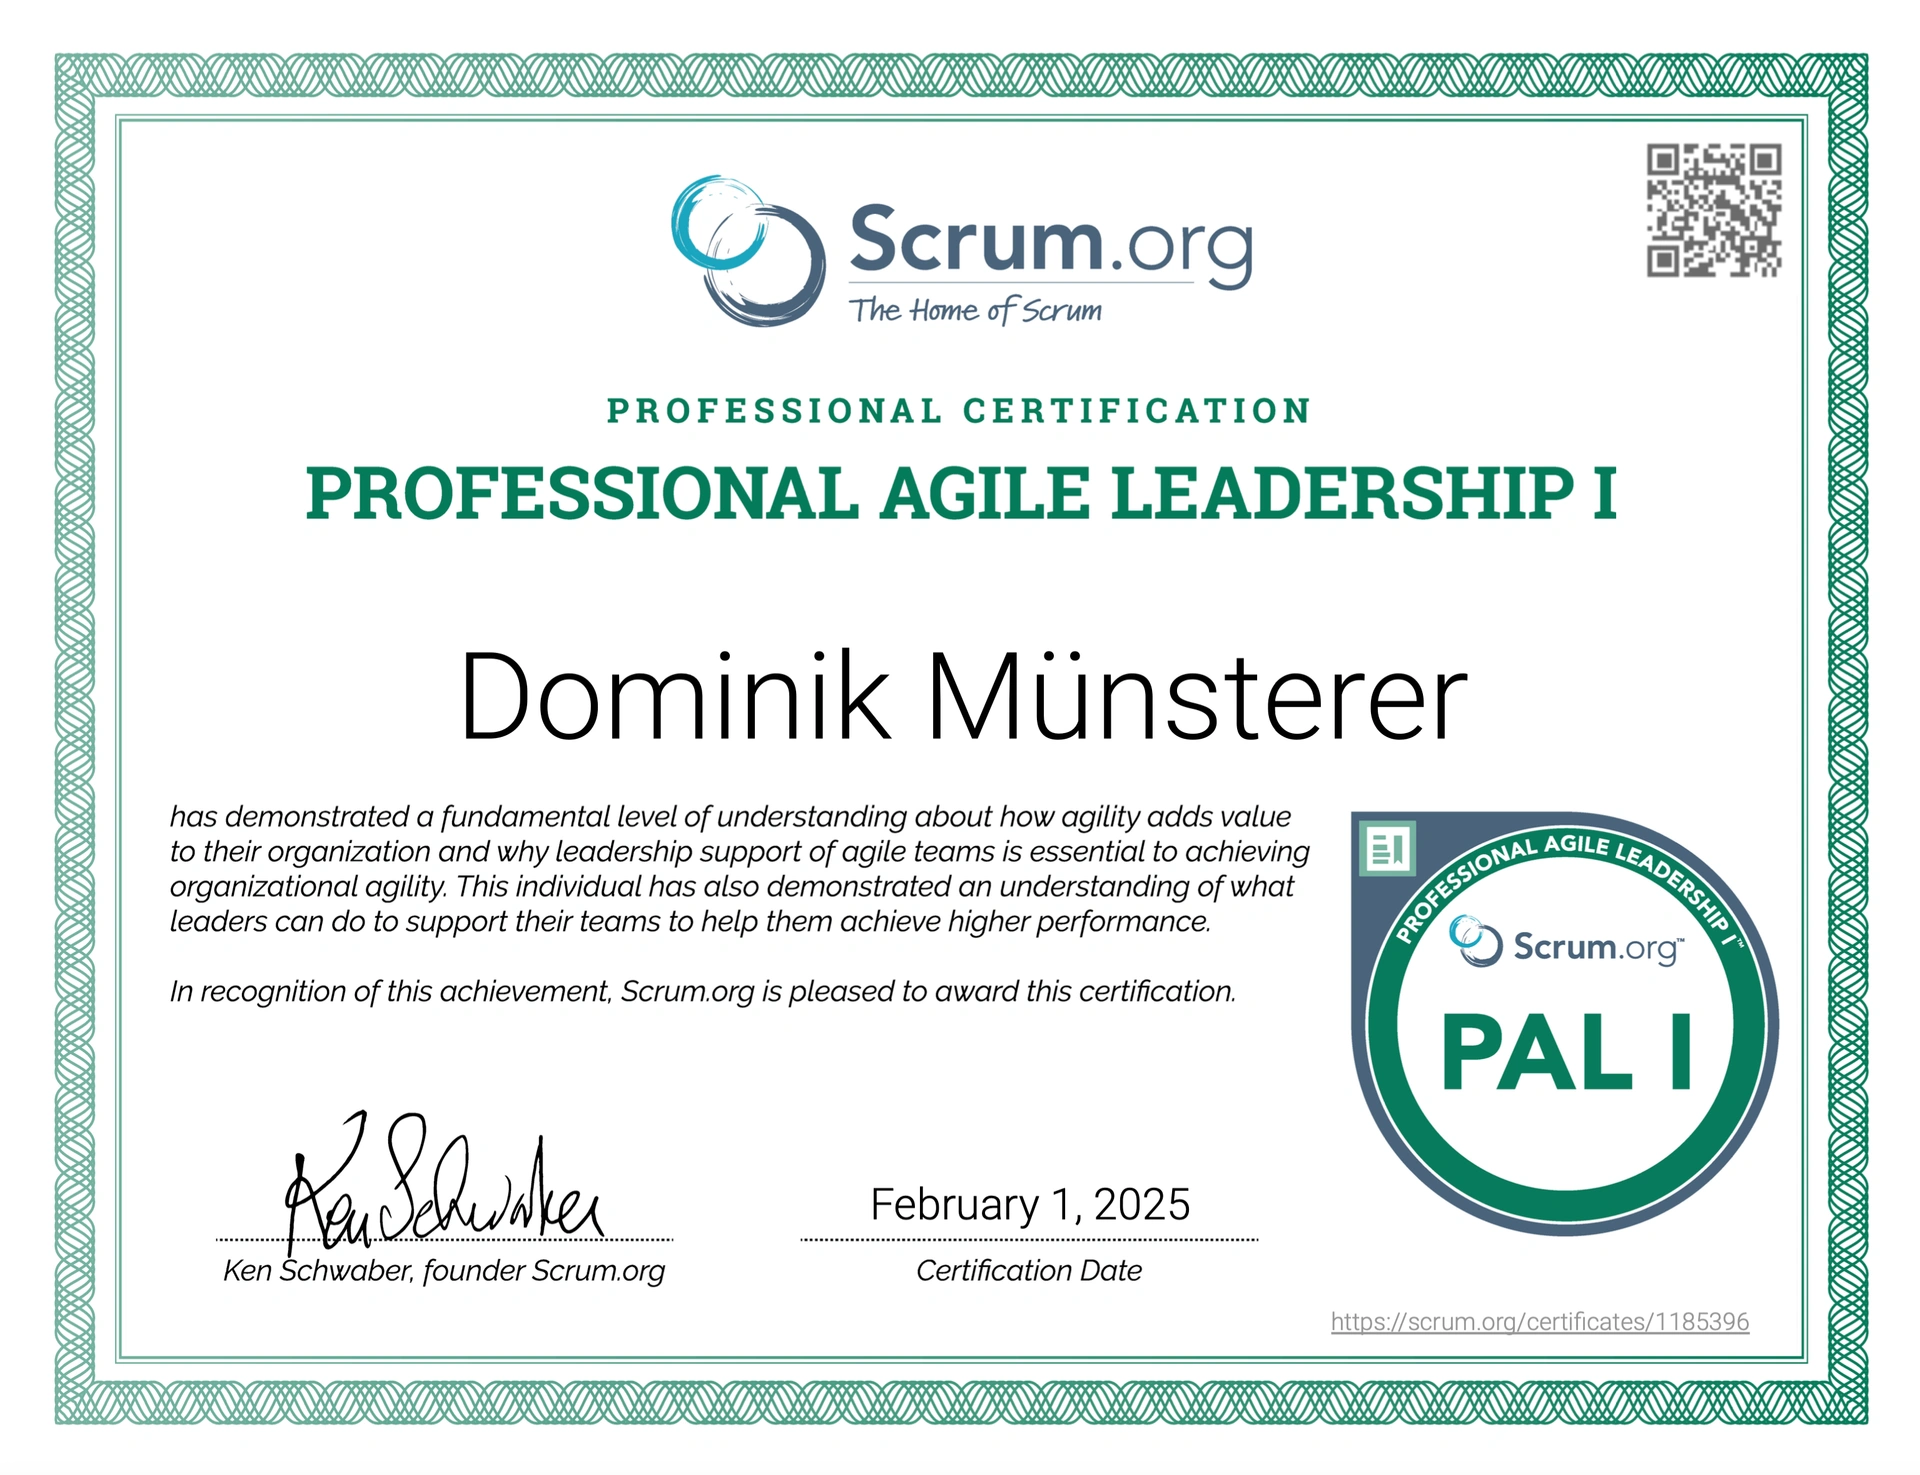
Scrum Professional Agile Leadership I (PAL I)
The Professional Agile Leadership I certification confirms solid knowledge in agile leadership and supporting teams in the adoption and scaling of agile methods.
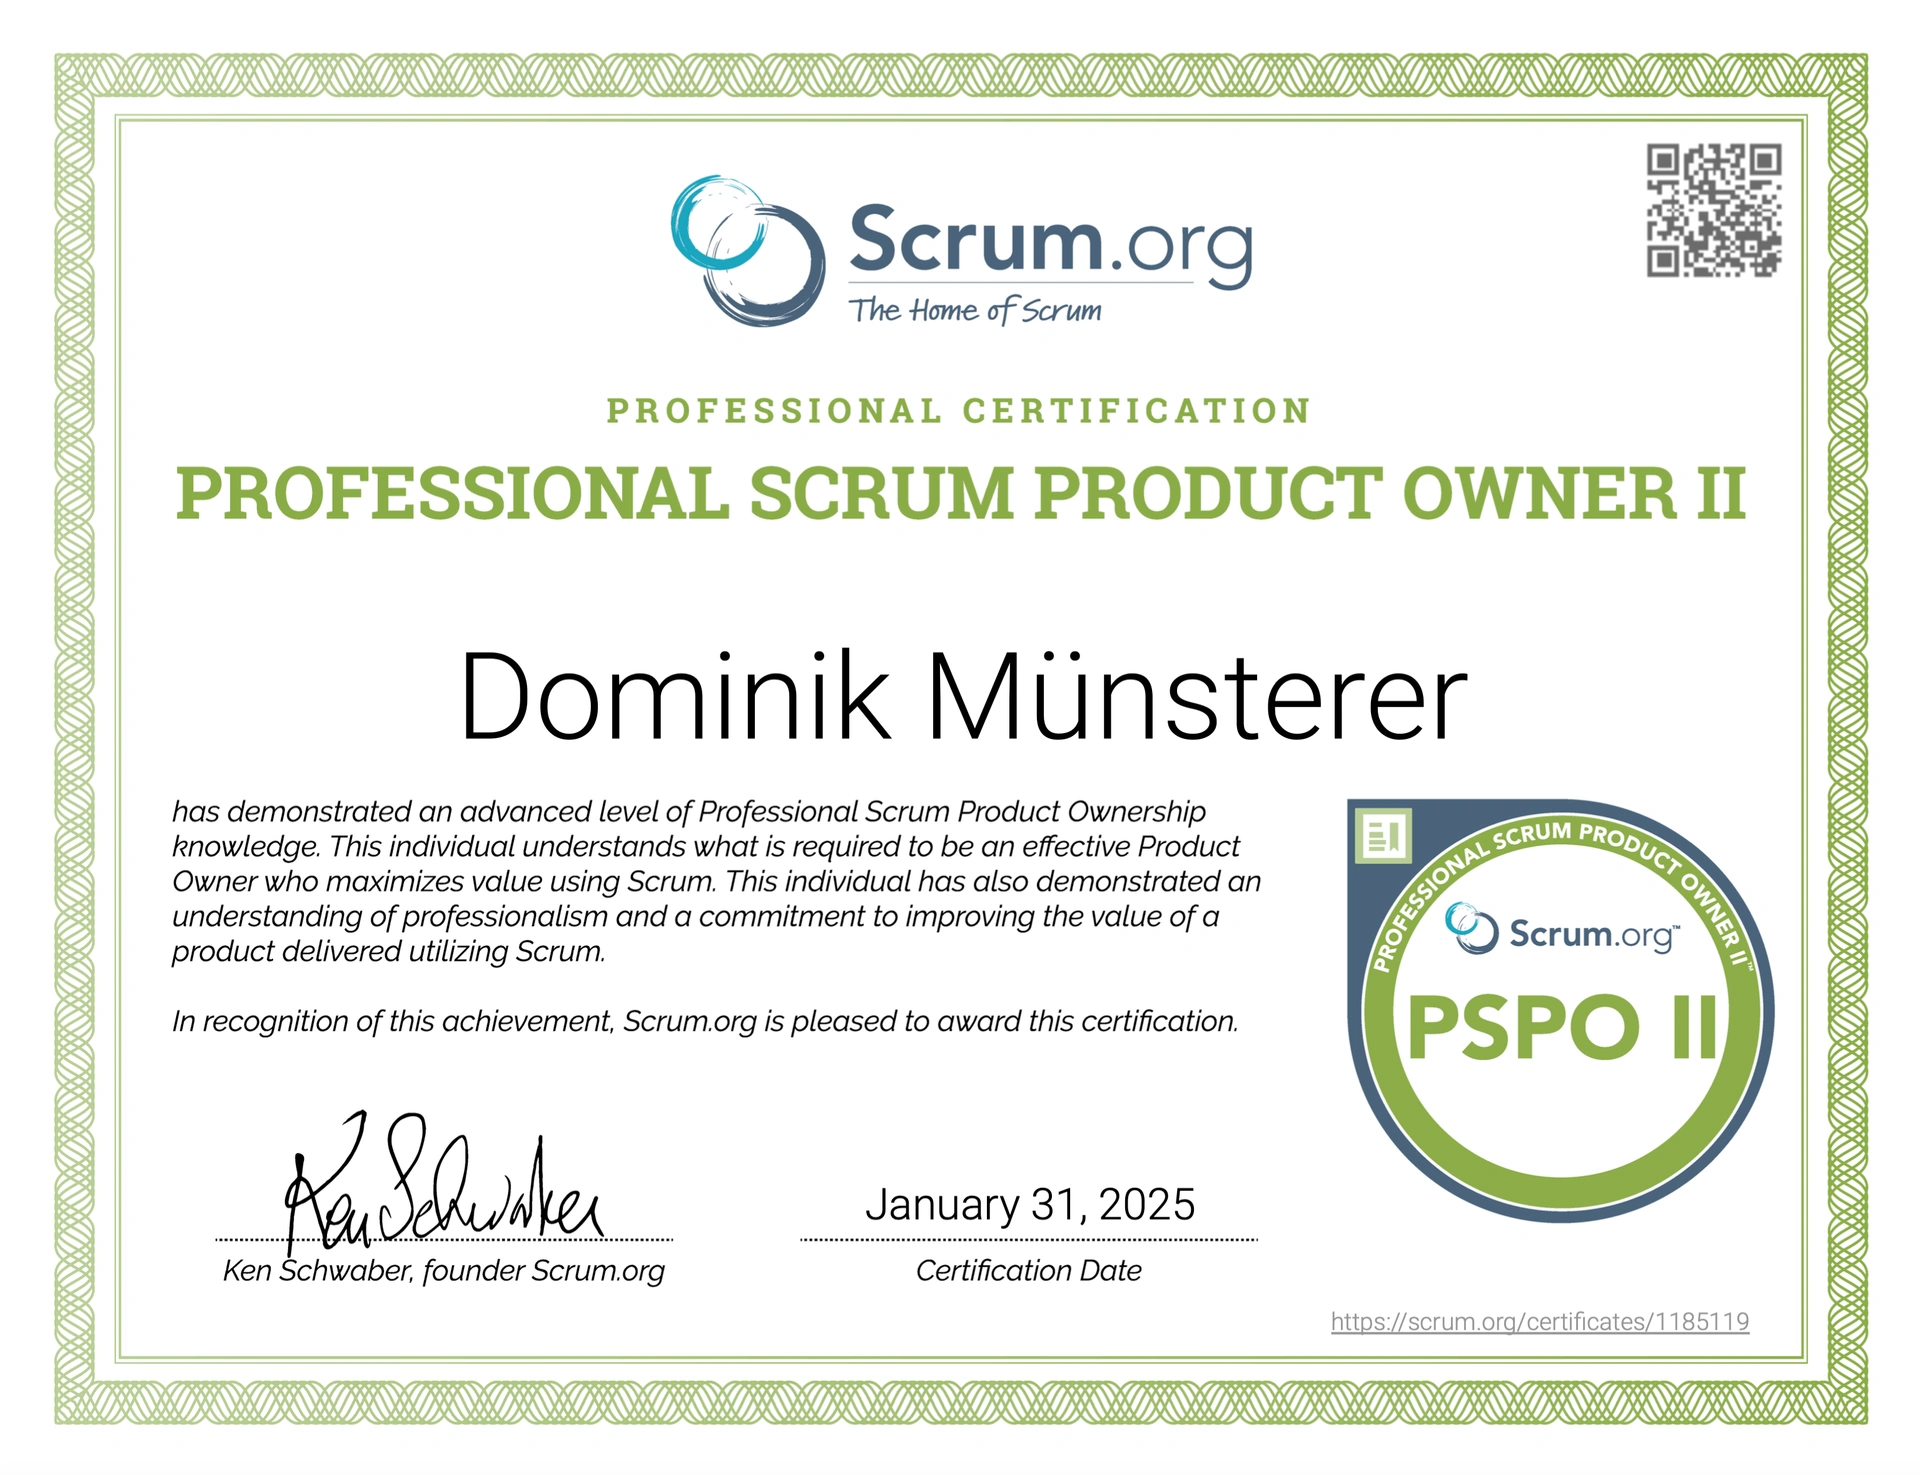
Professional Scrum Product Owner II (PSPO II)
The Professional Scrum Product Owner II certification confirms advanced skills in product strategy, stakeholder management, and value maximization within Scrum projects.
Cybersecurity is a matter of trust.
We firmly believe: Only the highest level of organizational and technological security, the highest availability, and the absolute integrity of data lead to the basis of any collaboration with our clients -- trust. Aus diesem Grund veröffentlichen wir unsereInformation Security Policy.
During the audits, our premises were inspected by PFI auditors and thoroughly examined for risks and countermeasures.
With the ISO/IEC 27001:2022 certification, we justify your trust in DeltaSecure going forward: in annual re-audits, the conformity of our company with ISO standards is regularly verified.
Because we see ourselves as a long-term reliable service provider that earns your trust every day through the quality of our services.
We develop exclusively meaningful and validated Service Level Agreements (SLAs) for you and naturally adhere to them strictly.
Commitment to quality
DeltaSecure GmbH provides consulting and service offerings for cybersecurity across various industries with high security requirements.
The requirements of our clients, partners, and our own standards demand the highest quality, robust security in information processing, and sustainable management of our environment and available resources.
As objective evidence of our trustworthiness, we have had our entire company certified under ISO/IEC 27001:2022 as part of our information security management -- i.e., across all processes, products, and services for all business areas. This system was audited by the Testing and Research Institute Pirmasens as a DAkkS-accredited, independent body.
Frequently Asked Questions
What ISO certification does DeltaSecure hold?
Which testing body conducted the audit?
What re-audit cycle applies?
What is the Hospital Future Fund authorization?
What personal certifications does the team hold?
Where can I find the certificates as PDFs?
Get in touch!
Contact us and we will provide a no-obligation quote. Is this an emergency? Use our 24/7 hotline.